Certifications
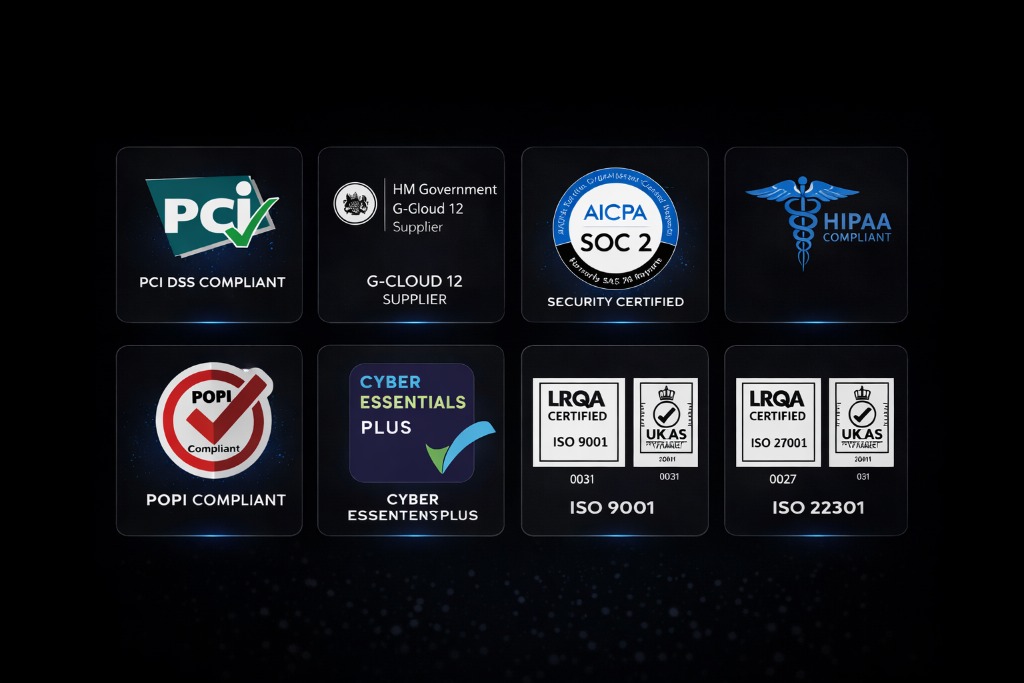
 PCI DSS Compliant
The Payment Card Industry Data Security Standard (PCI DSS) ensures that any system handling credit-card data follows strict security controls.
What this means for you: payment information is encrypted, securely processed, and protected against fraud or data leaks.
HM Government – G-Cloud 12 Supplier
Being a G-Cloud 12 Supplier means our services are approved for use by UK government bodies through the official Digital Marketplace.
What this means for you: our platform meets UK public-sector standards for security, reliability, and procurement transparency.
AICPA SOC 2 (Type II)
SOC 2, defined by the American Institute of Certified Public Accountants, evaluates how service providers manage customer data across five trust principles: security, availability, confidentiality, processing integrity, and privacy.
What this means for you: our internal controls are independently audited and proven effective over time—not just documented.
HIPAA Compliant
HIPAA (Health Insurance Portability and Accountability Act) governs how protected health information (PHI) is handled in the U.S.
What this means for you: if your workflows involve healthcare data, we support safeguards required to protect sensitive patient information and reduce compliance risk.
POPI (Protection of Personal Information Act) Compliant
POPI is South Africa's data-protection law, similar to GDPR. It regulates how personal data is collected, processed, stored, and shared.
What this means for you: personal data is handled lawfully, transparently, and with strong privacy protections—especially important for international operations.
Cyber Essentials Plus
Cyber Essentials Plus is a UK government-backed certification that goes beyond self-assessment and requires hands-on technical verification.
What this means for you: our systems are actively tested against common cyber threats such as malware, credential attacks, and misconfigurations.
LRQA Certified – ISO 9001
ISO 9001 focuses on quality management systems and operational consistency. Certification is issued by LRQA and accredited by UKAS.
What this means for you: our processes are structured, repeatable, continuously improved, and designed to deliver consistent service quality.
LRQA Certified – ISO/IEC 27001
ISO/IEC 27001 is the international standard for information security management systems (ISMS).
What this means for you: we formally identify, manage, and mitigate information-security risks across people, processes, and technology.
LRQA Certified – ISO 22301
ISO 22301 covers business continuity and operational resilience.
What this means for you: our platform is designed to remain available during incidents, disruptions, or failures—so your operations don't stop when something goes wrong.